To read the full article in our portal, and find an archive of related reporting, follow this link to - https://redskyalliance.org/xindustry/china-coverage-of-report-on-the-cyber-vulnerabilities-of-asian-po
Showing posts with label cyber attack. Show all posts
Wednesday, November 27, 2019
China Coverage of Report on the Cyber Vulnerabilities of Asian Ports
Labels:
China,
cyber attack,
cyber losses,
maritime
Monday, August 26, 2019
Cryxos Trojan Malware Uptick
Hackers can program Trojans like Cryxos to accomplish pretty much anything they want. In August 2019, Wapack Labs observed a significant uptick in malicious emails delivering a malware identified as Cryxos. The observed malware is currently being delivered to users in Brazil, however, thousands of related specimens were observed on Virus Total indicating a widespread campaign affecting multiple countries.To read the full article in our portal, and find an archive of related reporting, follow this link to - https://redskyalliance.org/finished-analysis/cryxos-variant
Friday, August 9, 2019
Health Center Gets Hit With Ransomware, Twice!
In April 2019, Park Duvalle Community Health Center (PDCHC), located in Louisville, KY was targeted with an unspecified variant of ransomware. It took PDCHC three weeks to restore their files from their back up and make the network fully functional. On June 7, 2019, PDCHC was hit again with ransomware, attackers requested a payment of approximately $70,000 worth of Bitcoin.
To read the full article in our portal, and find an archive of related reporting, follow this link to - https://redskyalliance.org/healthcare/
Labels:
Bitcoin,
cyber attack,
healthcare,
HIPPA,
Louisville KY,
PDCHC,
ransomware
Wednesday, June 28, 2017
Lurking Offshore: The Business Case Study for Working Together
Last week, the MPS-ISAO held a cybersecurity intelligence themed webinar, “Lurking Offshore: Active Cyber Threats Targeting Ports & Maritime”, with our partner, Wapack Labs. It’s a fascinating story about a financially motivated adversary using spear-phish to target Ports.I’m sure you are thinking, “Another scary cyber story… Why should I care?”By studying the data associated with this actor – how, when, why, and who, the case for Maritime and Port organizations working together to protect themselves from cyber adversaries is made. Cybersecurity silos need to be shattered - now.
Understanding the adversary.
Because Wapack has been tracking this adversary for some time, we have learned a lot by studying the intel.
First, this adversary is successful. Our intel team sees an almost 100% success rate with a low detection rate (< 5%) through traditional security technology and vendor sourced data. During the first six months of 2017, over 1,000 U.S. and European victims have been observed.
It’s a cost-effective, organized business operation. The malware being used only costs about $30 per month, and the adversary has developed a business model with specialized skills. Also, there is high reuse between victims. So, if one Port is compromised, there is a good possibility that other Ports will be targeted using the same spear-phish email.
And, this adversary is persistent. They improve odds of success by including supply chain partners in the scope of an attack. In one instance where a Port was the intended victim, ten suppliers to this Port were targeted at the same time and with the same spear-phish email being used across all organizations. The targeted suppliers were diverse too. They included organizations who performed:
- Construction Consortium
- Logistics Services
- Oil & Gas Services
- Consulting Services
- Marine Transport
- IT Services Provider
- Multi-Modal Transport
- Oil & Gas Engineering Services
Turning the tide.
In 2015, The Obama administration issued two important pieces of Cybersecurity legislation. A Presidential Executive Order (EO) was issued in February 2015 to promote private sector cybersecurity information sharing. Section 2 of this EO states, “strongly encourage the development and formation of Information Sharing and Analysis Organizations (ISAOs).” A few months later, the Cybersecurity Information Sharing Act of 2015 (CISA) was signed into law to “improve cybersecurity in the United States through enhanced sharing of information about cybersecurity threats.” CISA provides information sharing legal protections to organizations who participate in an ISAO.
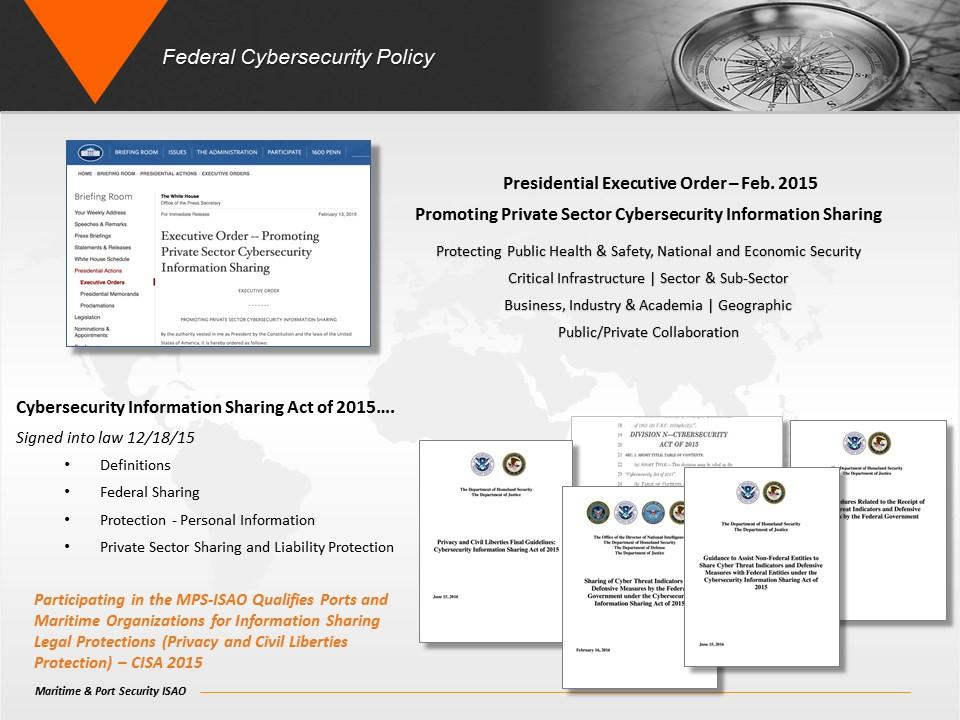
These two pieces of legislation led to the formation of the Maritime and Port Security ISAO, and its parent organization – the International Association of Certified ISAOs (IACI), to promote cyber resilience.
If someone could tell you where the sharks were, wouldn’t you want to know?
The MPS-ISAO, headquartered at the Global Situational Awareness Center (GSAC) at NASA/Kennedy Space Center, is a non-profit private sector-led organization working in collaboration with government to advance Port and Maritime cyber resilience. The core mission to enable and sustain a safe, secure and resilient Maritime and Port Critical Infrastructure through security situational intelligence, bi-directional information sharing, coordinated response, and best practice adoption supported by role-based education.
Port and Maritime organizations who subscribe to the MPS-ISAO’s cyber intelligence service have the advantage of early threat awareness provided via industry-specific, cross-sector, and global cyber intelligence along with countermeasure solutions. They participate in a Maritime and Port community composed of stakeholders from across the industry sector who are interested in working together to achieve cyber resilience.
Going back to the Lurking Offshore Case Study, we know that this adversary targets multiple victims within a Port’s supply chain using the same malicious email, and then reuses the email across another 8-10 Port victims. When the email is shared into the MPS-ISAO Community, early threat awareness enables organizations to put protective measures in place.
So, a single share can protect many.
And, the business case for working together was never stronger.
Wapack Labs’ engineers, researchers, and analysts design and deliver transformational cyber-security analysis tools that fuse open source and proprietary information, using deep analysis techniques and visualization. Information derived from these tools and techniques serve as the foundation of Wapack Labs’ information reporting to the cyber-security teams of its customers and industry partners located around the world.
Thursday, February 9, 2017
Maritime Shipping Concerns
Shipping companies investing in maritime port terminals may increase the risk of cyber-attacks. Such investments reduce costs associated with moving cargo, which can improve profitability. Two years of cheap credit and low fuel prices have propped up weaker carriers, lowered demand, and delayed mergers and alliances needed to resolve these concerns. An example: Hyundai Merchant bought a 20 % stake in Total Terminals International LLC from Mediterranean Shipping Co, who operates the Port of Long Beach. In addition to risks associated with integrating ship to shore cyber connections, adding another company (and its sub-contractors) to the corporate mix increases supply-chain risks.Wapack Labs has reported on maritime shipping in the past. An archive of related reporting can be found in the Red Sky Alliance Portal.
The following organizations were cited in this report: Hyundai Merchant, Port of Long Beach, Total Terminals International LLC
TLP: AMBER
ACTOR TYPE: (III)
SERIAL: TR-031-2017
COUNTRIES: US, KR, ES
INDUSTRIES: Maritime
REPORT DATE: 20170208
Labels:
cyber attack,
Hyundai,
maritime,
Port of Long Beach
Friday, October 28, 2016
Yevgeniy Nikulin - LinkedIn, Dropbox and Formspring
Wapack Labs has routinely exposed Russian malicious cyber activity. From the alleged Russian rigging of Ukrainian elections, electrical grid shutdowns and telecommunication manipulation to the recent hacking activity of Fancy Bear - Russia has been at the vortex of numerous cyber-attacks. This activity represents support of the Russian, “Ivanov Doctrine.” The current arrest of Yevgeniy Nikulin in the Czech Republic, who was indicted for the cyber- attacks of Linkedin, Formspring and Dropbox, highlights the gravity of Russian cyber activity. These attacks of big data companies have exposed Personally Identifiable Information (PII) and other breached data to unknown factions. This information is being supplied for your situational awareness.
- The “Ivanov Doctrine-New Generation Warfare,” was introduced in Russia approximately 15 years ago
- Russian cyber-attack activity has escalated in recent years.
- Yevgeniy Nikulin was arrested in the Czech Republic for hacking large U.S. data companies.
Publication
date: 26
October 2016
Handling
requirements: Traffic
light protocol (TLP) GREEN
Attribution/Threat
Actors: Yevgeniy Nikulin
Actor
Type: Adversary
capabilities have been assessed as Tier IV*
Potential Targets: U.S.
corporations (targeting PII)
Past Reporting: Red Sky Alliance: DOC-2183, DOC-
2349, DOC-2543, DOC-4287, Msgs #6498 #8612
* State actors who create vulnerabilities through an active program to “influence” commercial
products and services during design, development or manufacturing, or with the ability to impact
products while in the supply chain to enable exploitation of networks and systems of interest.
The full attribution report has been published in its entirety in the Red Sky Alliance portal. For more information please contact the lab directly at 844-4-WAPACK, 603-606-1246, or feedback@wapacklabs.com.
About Wapack Labs
Wapack Labs, located in New Boston, NH is a Cyber Threat Analysis and Intelligence organization supporting the Red Sky Alliance, the FS-ISAC and individual organizations by offering expert level targeted intelligence analysis answering some of the hardest questions in Cyber. Wapack Labs’ engineers, researchers and analysts use deep analysis techniques and visualization to design and deliver transformational cyber-security analysis tools that fuse open source and proprietary information. The intelligence derived from these tools and techniques serve as the foundation of Wapack Labs’ information reporting to the cyber-security teams of its customers and industry partners located around the world.
Labels:
cyber,
cyber attack,
Dropbox,
elections,
Fancy Bear,
Formspring,
Ivanov Doctrine,
LinkedIn,
PII,
Russia,
Ukrainian,
Yevgeniy Nikulin
Wednesday, October 5, 2016
Exploit Kit Author
Wapack
Labs has discovered an exploit kit author, selling within the Dark Web. Analysts
encountered this kit in September 2016, as the most popular/sought after
exploit kit amongst Brazilian hackers during the 2016 Rio Olympics. Wapack Labs analysts often research breaches of cyber security in numerous corporate and government cyber-attack incidents. This report contains identity, Dox and TTP information of actor - provided for your
situational awareness.
Publication
date: 03
October 2016
Handling requirements: Traffic light protocol (TLP) GREEN
Attribution/Threat Actors: Russian author
Actor Type: Adversary capabilities have been assessed as Tier IV*
Potential Targets: Worldwide individuals, corporation and/or governments
Past Reporting: N/A
*Criminal or state actors who are organized, highly technical, proficient, well-funded professionals working in teams to discover new vulnerabilities and develop exploits.
The full attribution report has been published in its entirety in the Red Sky Alliance portal. For more information please contact the lab directly at 844-4-WAPACK, 603-606-1246, or feedback@wapacklabs.com.
About Wapack Labs
Wapack Labs, located in New Boston, NH is a Cyber Threat Analysis and Intelligence organization supporting the Red Sky Alliance, the FS-ISAC and individual organizations by offering expert level targeted intelligence analysis answering some of the hardest questions in Cyber. Wapack Labs’ engineers, researchers and analysts use deep analysis techniques and visualization to design and deliver transformational cyber-security analysis tools that fuse open source and proprietary information. The intelligence derived from these tools and techniques serve as the foundation of Wapack Labs’ information reporting to the cyber-security teams of its customers and industry partners located around the world.
Labels:
brazil,
cyber attack,
dark web,
dox,
exploit kit,
hacker,
ttp
Subscribe to:
Posts (Atom)